Connecting your website to Cloudflare is the single most impactful optimization you can execute to accelerate page load times, slash server bandwidth costs, and shield your domain against DDoS assaults and malicious vulnerability scanners. Cloudflare acts as an intelligent reverse proxy that sits between your website’s origin server and public visitors, filtering out malicious bot traffic while caching static assets at over 330 edge data centers worldwide. In this step-by-step engineering walkthrough, we guide you through the entire onboarding process—from account creation and DNS record migration to SSL configuration and edge caching rules.
1. Step 1: Creating a Cloudflare Account & Adding Your Domain
Begin by navigating to Cloudflare’s official sign-up portal. Enter your email and create a secure password. Once logged into the Cloudflare dashboard:
- Click “Add a Site” in the top-right navigation.
- Enter your root domain name (e.g.
yourdomain.com) withouthttps://orwww. - Select the Free Plan (or Pro plan if you require advanced image optimization and mobile redirect rules) and click Continue.
To understand why edge routing is so critical for business scalability, review our comprehensive analysis on why Cloudflare is the best CDN for modern websites.
2. Step 2: Verifying and Configuring DNS Records
Cloudflare will automatically query global DNS servers and import your domain’s existing DNS records. Carefully review every imported row:
- A Records & CNAMEs: Ensure your primary
@(root) andwwwrecords point to your correct web host IP address. Confirm that the proxy status is toggled to Orange Cloud (Proxied) to enable CDN caching and WAF security. - Mail Records (MX): Mail records (e.g., Google Workspace, Office 365, or host cPanel mail) must ALWAYS remain Gray Cloud (DNS Only). Cloudflare proxies HTTP/HTTPS web traffic only; proxying mail records will break incoming email delivery.
- TXT Verification Records: Ensure SPF, DKIM, DMARC, and Google site verification records are fully present.
3. Step 3: Updating Nameservers at Your Domain Registrar
To route incoming web traffic through Cloudflare’s edge network, you must delegate authoritative DNS management. Cloudflare will assign two unique nameservers (such as ns1.cloudflare.com and ns2.cloudflare.com).
- Log into your domain registrar (e.g. GoDaddy, Namecheap, Google Domains / Squarespace, or Hostinger).
- Navigate to your domain’s DNS / Nameservers management section.
- Switch from “Default Nameservers” to “Custom Nameservers” and paste the two Cloudflare nameserver addresses.
- Save your changes. Global DNS propagation typically takes between 10 minutes and 24 hours.
4. Step 4: Configuring SSL/TLS Encryption (Full Strict)
In the Cloudflare dashboard, navigate to SSL/TLS > Overview. You will see four encryption modes. Always select “Full (Strict)”:
Off            -> No encryption (Insecure)
Flexible       -> Encrypted between Browser and Cloudflare, UNENCRYPTED to Origin (Dangerous)
Full           -> Encrypted end-to-end, accepts self-signed origin certificates
Full (Strict)  -> Encrypted end-to-end with verified SSL on origin server (Industry Standard)
Warning: Avoid using “Flexible” mode with WordPress, as it frequently triggers infinite 301 redirect loops. Ensure your server enforces strict transport security by reviewing our guide on adding HTTP security headers in WordPress.
5. Step 5: Speed Optimization & Edge Caching Directives
Navigate to Speed > Optimization and activate these high-impact toggles:
- Brotli Compression: Delivers superior asset compression compared to legacy Gzip, reducing CSS and JS byte payloads by up to 20%.
- Early Hints (103): Preloads critical font and stylesheet assets while the server processes dynamic requests.
- Auto Minify: Minifies HTML, CSS, and JS at the edge without requiring bloated WordPress caching plugins. For asset delivery optimization, review our guide on disabling lazy loading on hero images.
6. Step 6: Hardening Origin Security & WAF Rules
Under Security > WAF > Custom Rules, construct custom firewall rules to block malicious crawlers from probing vulnerable endpoints:
Rule Name: Block AI Crawlers on Login
Expression: (http.request.uri.path contains "/wp-login.php" and cf.bot_management.score < 30)
Action: Block
Learn more about blocking automated exploit attempts in our technical guide on defending WordPress origins against AI automated vulnerability scanners. If configuration errors ever cause database lockouts, consult our troubleshooting guide on how to fix 'Error Establishing a Database Connection' in WordPress.
Conclusion
In conclusion, mastering how to add cloudflare to your website: a step-by-step guide is essential for building a resilient, high-performing WordPress website. By implementing the architectural best practices and configurations covered in this guide, you ensure your platform maintains peak performance, bulletproof security, and seamless user experiences.
Continuously auditing your server configurations, monitoring error logs, and adhering to clean development standards will keep your site reliable as your business scales. Investing in high-performance hosting and modern engineering prevents costly downtime and maximizes your digital investment.
At Vox Weebly, we understand the importance of a fast, secure, and custom-engineered WordPress website, and our team of senior developers can help you build, optimize, and maintain your web platform for maximum performance. Contact us today to learn more about our custom WordPress website development services.
7. Frequently Asked Questions (FAQ)
Will adding Cloudflare break my WordPress admin dashboard?
No. When configured with "Full (Strict)" SSL and standard bypass rules for /wp-admin/, Cloudflare accelerates dashboard asset delivery while shielding your login endpoint against brute-force assaults.
How do I purge Cloudflare cache after updating my website?
Navigate to Caching > Configuration > Purge Cache in the Cloudflare dashboard and select "Purge Everything", or use automated API cache-purge integration within your WordPress theme.
Cloudflare Page Rules and Cache-Everything Configurations
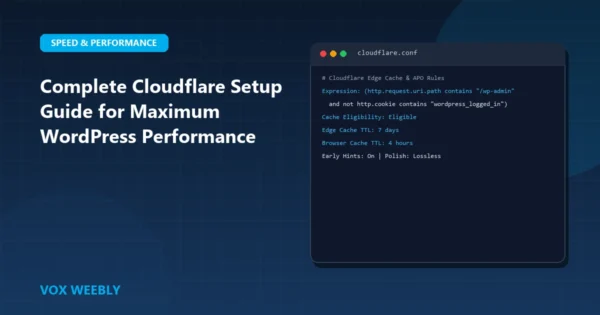
To achieve sub-100ms TTFB globally, configure Cloudflare Page Rules to enforce edge caching across your entire WordPress blog. Navigate to Rules > Page Rules and create a rule matching your blog directory:
URL: https://voxweebly.com/blog/*
Settings:
  Cache Level: Cache Everything
  Edge Cache TTL: 7 days
  Browser Cache TTL: 4 hours
Ensure you add a higher-priority bypass rule for /wp-admin/* and /*preview=true* so administrative operations and drafts are never cached at the edge. For official configuration patterns, explore Cloudflare Page Rules Developer Documentation.
Cloudflare Tiered Caching & Argo Smart Routing
For websites serving a global user base, enabling Tiered Caching organizes Cloudflare edge data centers into a hierarchical topology. When an edge node in a smaller city experiences a cache miss, it queries an upper-tier regional hub data center rather than routing back to your origin server, boosting origin cache hit ratios to over 95%.