In today’s fast-evolving cybersecurity landscape, website security is of paramount importance for business owners, e-commerce stores, and digital agencies. WordPress powers over 43% of the web, making it a frequent target for automated bots, cross-site scripting (XSS) vectors, and clickjacking attacks. One of the most effective, low-overhead methods to dramatically harden your WordPress website is by implementing HTTP Security Headers.
These headers provide instruction sets directly to client web browsers on how to handle your site’s content, scripts, iframes, and connections securely. In this comprehensive technical guide, we will break down the six most critical security headers, demonstrate three distinct implementation methods (PHP functions.php, Apache .htaccess, and Nginx), and show you how to achieve an A+ rating on SecurityHeaders.com.
To protect your server origin against automated botnets and zero-day probes, pair these headers with our comprehensive guide on defending WordPress origins against AI vulnerability scanners.
Why Are HTTP Security Headers Critical for Business Websites?
When a browser requests a page from your WordPress server, the server responds with the HTML content alongside HTTP response headers. By default, standard WordPress installations omit several crucial defensive headers, leaving user sessions and page elements susceptible to malicious exploitation.
Implementing security headers delivers three core advantages:
- Defeating Clickjacking and UI Redress Attacks: Attackers can embed your website inside a transparent iframe on a malicious domain, tricking logged-in administrators or customers into clicking buttons they didn’t intend to click (such as deleting data or authorizing payments).
- Preventing Cross-Site Scripting (XSS) and Injections: Enforcing strict Content Security Policies ensures that browsers only execute authorized scripts originating from trusted domains.
- Stopping MIME-Type Sniffing: Browsers sometimes attempt to guess the content type of files rather than respecting the server header, which attackers exploit to execute disguised malicious JavaScript disguised as an image file.
- Mandatory SSL/TLS Encryption: With HSTS enabled, browsers are strictly instructed never to communicate with your domain over unencrypted HTTP, mitigating man-in-the-middle (MITM) credential interception.
The 6 Essential HTTP Security Headers Explained
1. X-Frame-Options
The X-Frame-Options header tells the browser whether your site is allowed to be rendered within a <frame>, <iframe>, <embed>, or <object> tag. To protect your site against clickjacking, you should set this header to SAMEORIGIN. This allows framing only by pages on the exact same origin as the site itself.
2. X-Content-Type-Options
Setting X-Content-Type-Options: nosniff forces modern browsers to respect the MIME types advertised in the Content-Type headers. If a user uploads an avatar that contains executable JavaScript, the browser will refuse to treat it as script code, completely neutralizing malicious execution attempts.
3. Strict-Transport-Security (HSTS)
HTTP Strict Transport Security (HSTS) enforces encrypted HTTPS connections between visitors and your web server. It prevents protocol downgrade attacks and cookie hijacking. A robust production HSTS header includes a 1-year max-age (31536000 seconds), includes all subdomains, and requests preloading into major browser vendor lists.
4. Content-Security-Policy (CSP)
The Content-Security-Policy (CSP) header is considered the gold standard of modern front-end application security. It provides a granular allowlist detailing exactly where scripts, styles, fonts, images, and media are allowed to load from. While powerful, CSP must be configured carefully to avoid blocking necessary third-party assets such as Google Analytics, Google Fonts, or payment gateways.
5. Referrer-Policy
The Referrer-Policy header controls how much referrer information (the URL of the page where a visitor clicked a link) is sent along with requests. Setting this to strict-origin-when-cross-origin protects sensitive customer query parameters and internal URLs from leaking to external third-party servers.
6. Permissions-Policy (Formerly Feature-Policy)
The Permissions-Policy header allows website owners to selectively enable or disable browser hardware features and APIs, such as the visitor’s camera, microphone, geolocation sensor, and payment request API. For a standard business or e-commerce site, restricting these APIs by default reduces attack surface area to zero.
Method 1: Implementing Headers in WordPress via functions.php (Recommended)
The cleanest, platform-independent way to register HTTP security headers is by hooking into the WordPress send_headers action inside your custom theme or child theme’s functions.php file. This ensures headers are sent dynamically across all WordPress page templates.
Add the following code snippet to your theme’s functions.php file:
// Hardening WordPress with Custom HTTP Security Headers
function voxweebly_add_security_headers() {
    // Prevent Clickjacking
    header( 'X-Frame-Options: SAMEORIGIN' );

    // Prevent MIME-Type Sniffing
    header( 'X-Content-Type-Options: nosniff' );

    // Enable XSS Filtering in legacy browsers
    header( 'X-XSS-Protection: 1; mode=block' );

    // Restrict Referrer Information on External Navigation
    header( 'Referrer-Policy: strict-origin-when-cross-origin' );

    // Restrict Hardware Sensors & Geolocation APIs
    header( 'Permissions-Policy: geolocation=(), camera=(), microphone=(), payment=()' );

    // Enforce HTTPS Connections (HSTS - 1 Year)
    if ( is_ssl() ) {
        header( 'Strict-Transport-Security: max-age=31536000; includeSubDomains; preload' );
    }
}
add_action( 'send_headers', 'voxweebly_add_security_headers' );
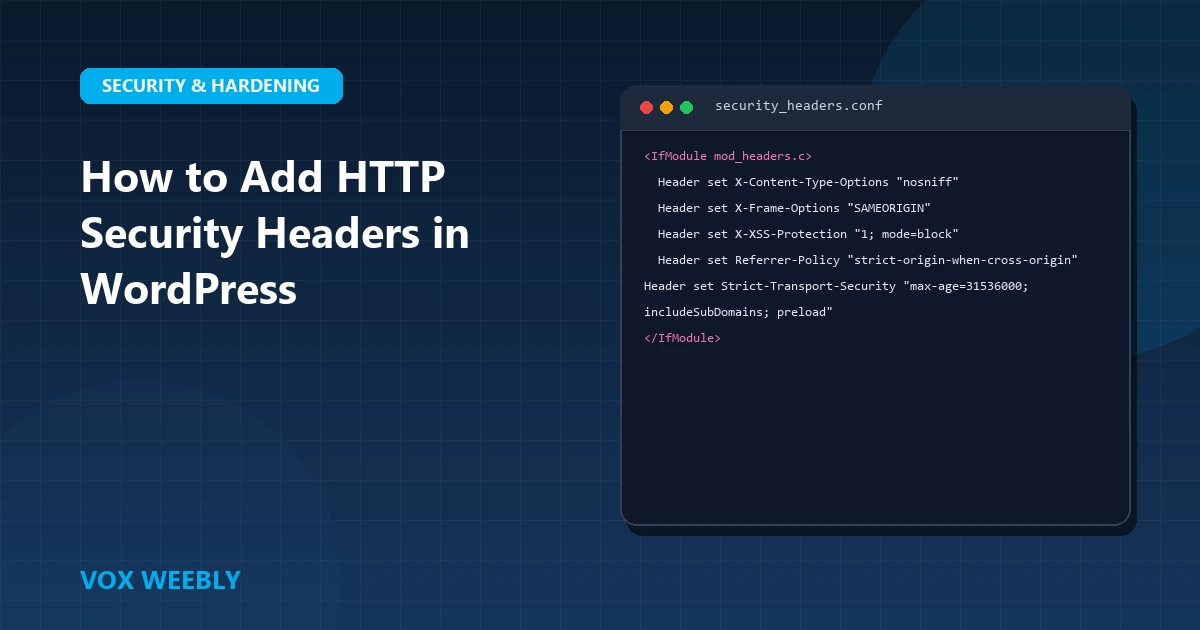
Method 2: Adding Headers via Apache .htaccess File
If your WordPress website is hosted on an Apache or LiteSpeed server (such as SiteGround, Hostinger, or cPanel hosting), adding headers via .htaccess allows the web server to emit headers even before WordPress finishes booting, providing maximum performance efficiency.
Open your website’s root .htaccess file and paste the following block above the # BEGIN WordPress line:
<IfModule mod_headers.c>
    Header always set X-Frame-Options "SAMEORIGIN"
    Header always set X-Content-Type-Options "nosniff"
    Header always set X-XSS-Protection "1; mode=block"
    Header always set Referrer-Policy "strict-origin-when-cross-origin"
    Header always set Permissions-Policy "geolocation=(), camera=(), microphone=()"
    Header always set Strict-Transport-Security "max-age=31536000; includeSubDomains; preload" env=HTTPS
</IfModule>
Method 3: Configuring Headers in Nginx Server Blocks
For high-traffic enterprise WordPress setups running on Nginx (such as Cloudways, RunCloud, or DigitalOcean LEMP stacks), security headers should be configured directly within your domain server block or nginx.conf file:
# Nginx Server Block Security Headers Configuration
add_header X-Frame-Options "SAMEORIGIN" always;
add_header X-Content-Type-Options "nosniff" always;
add_header X-XSS-Protection "1; mode=block" always;
add_header Referrer-Policy "strict-origin-when-cross-origin" always;
add_header Permissions-Policy "geolocation=(), camera=(), microphone=()" always;
add_header Strict-Transport-Security "max-age=31536000; includeSubDomains; preload" always;
After editing, remember to run sudo nginx -t to verify syntax before reloading with sudo systemctl reload nginx.
How to Verify and Test Your HTTP Security Headers
Once you have implemented your security headers, it is essential to verify that your web server is delivering them properly without duplicate conflicts.
1. Testing with cURL in Terminal
You can instantly view your active response headers by running the following command in PowerShell, Terminal, or Command Prompt:
curl -I https://yourwebsite.comInspect the output list to verify that x-frame-options, x-content-type-options, and strict-transport-security are returned with status HTTP/2 200.
2. Online Testing Tools
Visit SecurityHeaders.com and enter your website URL. This free security tool evaluates your configuration against global security benchmarks and awards an A+ rating when all essential headers are correctly set up.
Common Pitfalls and How to Avoid Them
- Breaking Elementor or Page Builder Previews: If you use page builders that render edit interfaces in iframes across different subdomains,
X-Frame-Options: SAMEORIGINmight block preview mode. In such cases, specify allowed domains inside yourContent-Security-Policyframe-ancestors directive. - Duplicate Header Values: Setting headers in both
.htaccessand your WordPress theme can cause duplicate headers (e.g.SAMEORIGIN, SAMEORIGIN), causing browsers to disregard the rule entirely. Choose one unified location to manage headers. - Enabling HSTS Without Working SSL: Never deploy HSTS if your SSL certificate is unstable or nearing expiration, as visitors will be permanently blocked from accessing your website until a valid certificate is installed.
Frequently Asked Questions (FAQ)
Do HTTP security headers affect WordPress SEO rankings?
Yes, directly and indirectly. Google prioritizes website security, user privacy, and HTTPS enforcement as part of its Page Experience signals. Websites with robust security headers avoid malicious script injections and malware blacklisting that can devastate organic search visibility.
Can security headers slow down my WordPress page load time?
No. HTTP security headers consist of lightweight text strings returned in the initial server handshake. They introduce zero perceptible latency and often improve overall client-side rendering speed by instructing the browser precisely how to process resources safely.
Should I use a security plugin instead of code?
While security plugins like Wordfence and iThemes Security can configure basic headers, implementing them directly via your custom theme’s functions.php or server config avoids plugin bloat, reduces database queries, and keeps your codebase clean and lightweight.
Conclusion: Build a Fortified WordPress Foundation
Securing your WordPress website is an essential ongoing practice that protects your brand reputation, customer data, and search engine standing. By implementing standard HTTP security headers, you eliminate vast categories of common web vulnerabilities with just a few lines of clean code.
At Vox Weebly, we build performance-first, custom ACF WordPress themes that include built-in enterprise security standards from day one. If you need assistance securing your corporate website, auditing Core Web Vitals, or migrating away from bloated page builders, our team of seasoned engineers is ready to help.
Note: If server misconfigurations during header editing ever trigger an unexpected downtime or database timeout, refer to our step-by-step tutorial on how to fix ‘Error Establishing a Database Connection’ in WordPress.